


Security Workflow Integration for Cortex XDR
When EDR and XDR tools raise alerts, you can use automated workflows in Blink to quickly gather info on IOCs, quarantine devices, and notify the relevant team members.
Automating Cortex XDR Security Workflows with Blink
Blink supports 14 out-of-the-box actions for Cortex XDR services so it’s easy to respond to malware alerts with smart, automated workflows.
Cortex XDR enables organizations to protect devices by monitoring for viruses and malware. With automated workflows in Blink, security teams can streamline their process for investigating and responding to these emerging threats. When isolating devices and aggregating information about IOCs is automatic, security teams can quickly mitigate organizational risk.
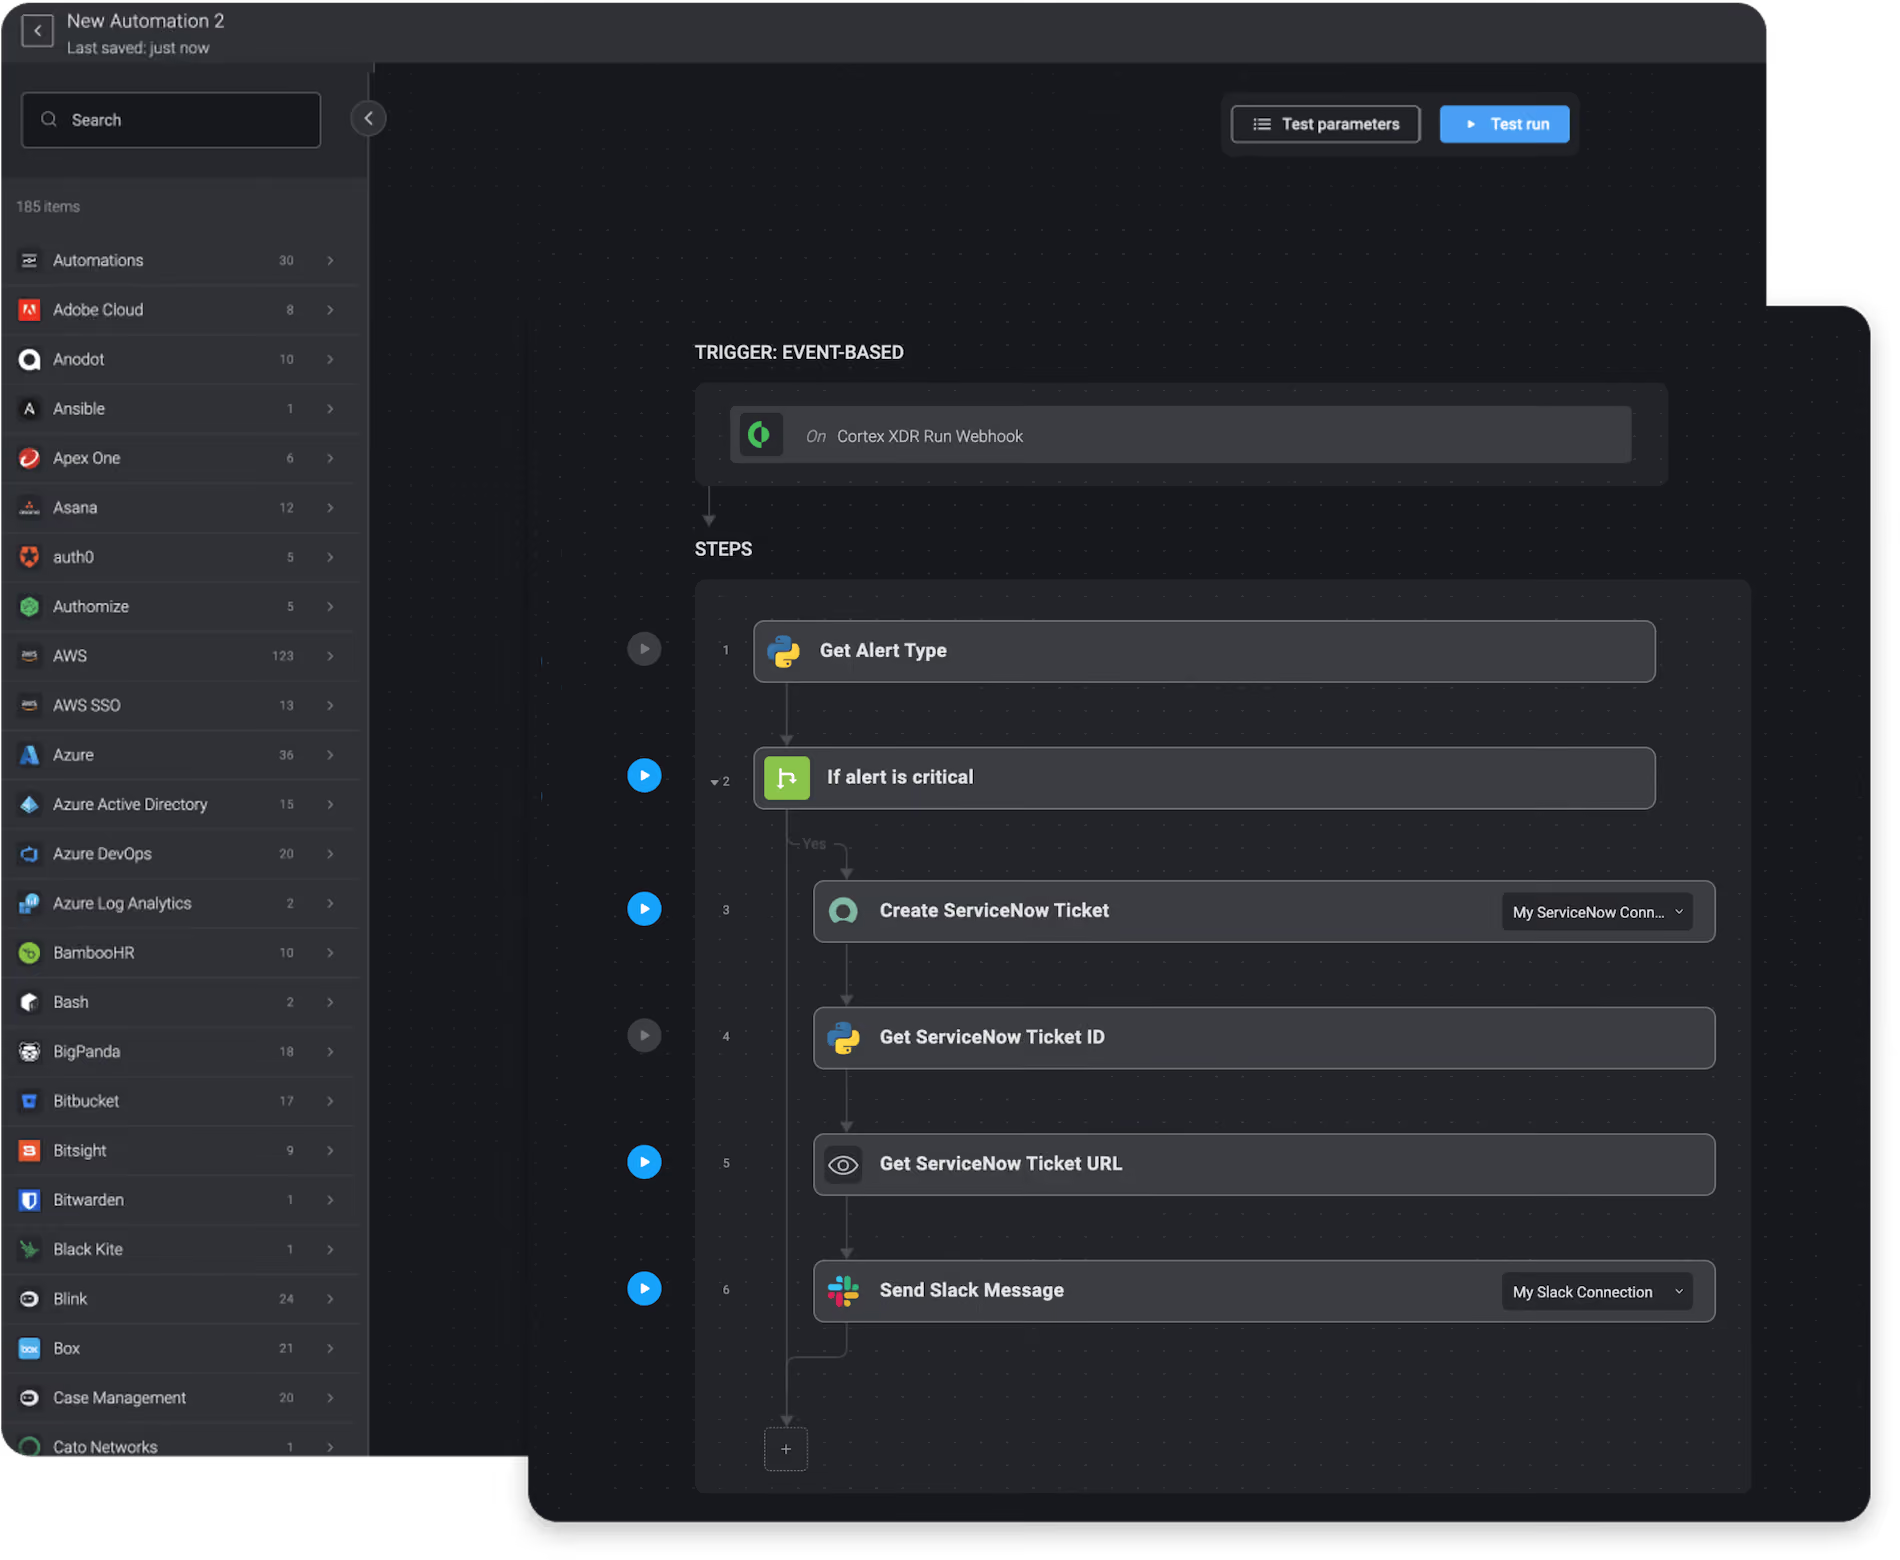
For structured, repeatable tasks that need to run the same way every time, Blink offers deterministic workflows built on the same Cortex XDR actions. No reasoning required, just reliable execution on a defined path. In the Blink library, we have compiled 8,000 automations that customers can download and run instantly. These automations include workflows for cloud security, compliance, identity & access management, network security, SOC & incident response, and threat hunting.
Incident Response & Case Management


Scan Endpoint with Cortex XDR and Send Results via Email
Get Scan Status with Cortex XDR and Send Results via Email
Isolate Endpoint with Cortex XDR and Send Results via Email
Execute Python Script with Cortex XDR and Send Results via Email
Add Files to Block List with Cortex XDR and Send Results via Email
Retrieve Files from Endpoint with Cortex XDR and Send Results via Email


